[Bug] Docker entrypoint auth bootstrap is unsafe for mounted and upgraded configs
Maintainer thường phản hồi trong vòng 1 ngày
Chưa có ai nhận issue này.
Đánh giá
- Độ khó
- 5/5
- Thời gian dự kiến
- Hơn một tuần
- Mức phù hợp với người mới
- 45/100
Hướng nghiên cứu
Bắt đầu với docker-entrypoint.sh và bin/enable-auth.sh để theo dõi quy trình bootstrap xác thực hiện tại và các đường dẫn viết lại thuộc tính. Sau đó kiểm tra phạm vi config CLI được đề xuất, bộ kiểm thử entrypoint và các bộ lọc đường dẫn trong docker-build-ci.yml. Được xem là hoàn tất khi các cấu hình được mount và được nâng cấp được xử lý nhất quán, các secret không bị lộ dưới dạng đối số tiến trình, và các bài kiểm thử shell được liệt kê bao phủ contract của entrypoint.
Do mô hình lập chỉ mục viết ra từ nội dung của issue.
Mô tả
Problem
The Docker entrypoint bootstraps authentication with grep/sed against
conf/rest-server.properties. That works for the shipped defaults it was
written for, but not for mounted configs, upgraded volumes, or any value whose
encoding differs between shell and HugeConfig.
Concrete cases, most of them raised during review of #3119:
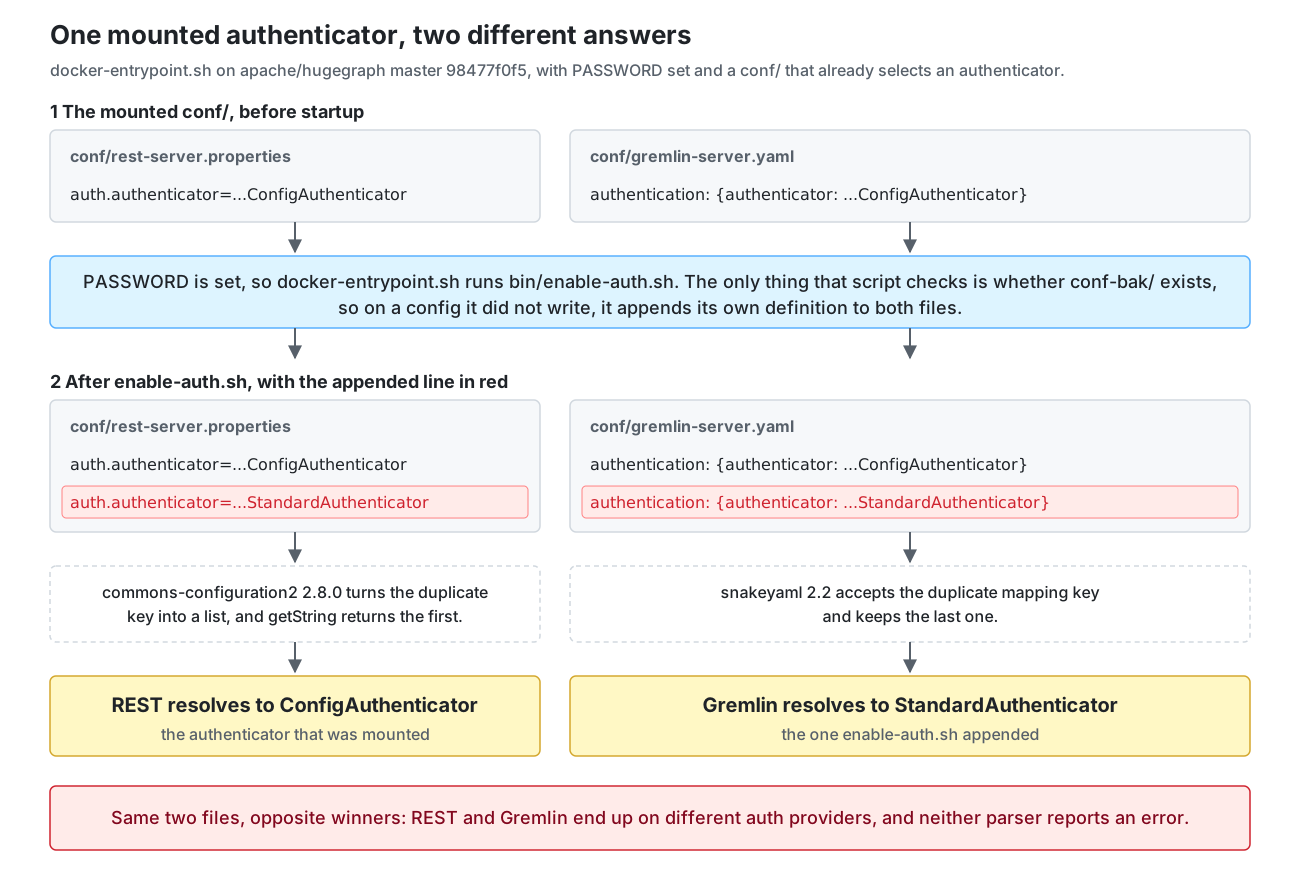
- Gremlin and REST can end up on different auth providers. The check is a
presence-onlygrepforauth.authenticator, so a config that already has
the REST property but not the Gremlin side is treated as fully configured. - A pre-existing authenticated volume can fail its first startup after
upgrade. A legacy volume can carrydocker/init_completewhile the
bootstrap state the entrypoint now expects is absent. PASSWORDis observable. It is currently handed to Java as a command-line
argument, which puts it inpsoutput for every process in the container.sedrewriting does not implement the Java properties grammar. Escaped
keys,:and whitespace separators, continuations, and duplicate logical
definitions are all read differently byHugeConfigthan by the entrypoint.
Concretely,set_propdetects onlykey=, so a mounted config using:
gets a second logical definition appended andHugeConfigthen rejects the
file as a list. This affectsbackendandpd.peersas well as
init_store.enabled, so the fix should cover all of them together.PASSWORDsilently does nothing when init-store is skipped.init-store
reads it from stdin, and the disabled path returns before that, so the admin
is created on the PD startup path fromauth.admin_pa— public defaultpa.
#3119 documents this and warns at runtime; it does not fix it.
The first case, as it stands on master 98477f0f5: the entrypoint no longer
greps for auth.authenticator itself, it calls bin/enable-auth.sh whenever
PASSWORD is set, and that script gates only on whether conf-bak/ exists.
On a config it did not write, it appends a second definition to both files,
and the two parsers disagree about which one wins.
Proposal
Move property reading and writing off grep/sed and onto the same
Commons Configuration path HugeConfig uses, so both sides agree on encoding,
and let the entrypoint delegate auth classification to it.
Rough shape:
- a small
ConfigToolCLI for typed get/set against a properties file,
preserving comments, file mode, and inode for mounted configs; - entrypoint uses it instead of
grep/sed, and stops passing secrets as
process arguments; - auth bootstrap becomes explicit about mounted, upgraded, and custom
authenticator cases rather than inferring from one key's presence; - a shell test suite covering the entrypoint contract, wired into
docker-build-ci.yml.
Scope
In scope: docker-entrypoint.sh, the new config CLI and its wrapper, the
entrypoint test suite, and the workflow path filters that run it.
Out of scope: the init_store.enabled option and its gate (#3118 / #3119),
Helm chart structure, and GraphManager behavior.
Context
This work originally shared a branch with #3119. That made a ~2,900-line diff
covering two unrelated ideas, so it was split out to keep each reviewable on
its own. #3119 now carries only the option, the gate, the env mapping, and the
init-flag guard.
Visual summary
- Ngôn ngữ chính
- Java
- Star
- 3.2k
- Fork
- 637
- Merge trung bình
- 3 ngày 17 giờ
- Pull request đã merge (30 ngày)
- 22
Chuẩn bị môi trường
Bắt đầu từ đâu
- Đọc hết issue, rồi đọc hướng dẫn đóng góp của dự án.
- Bình luận trên issue rằng bạn sẽ nhận — tránh hai người làm cùng một việc.
- Fork repository và làm thay đổi trên một nhánh.
- Mở pull request có tham chiếu số hiệu của issue.
Issue khác của apache/hugegraph
-
Độ khó 2/5 1-3 giờ Mức phù hợp với người mới 70/100
apache/hugegraph#3231 · 1 bình luận ·
Maintainer thường phản hồi trong vòng 1 ngày
-
bug
Độ khó 2/5 1-3 giờ Mức phù hợp với người mới 64/100
apache/hugegraph#3142 · 7 bình luận ·
Maintainer thường phản hồi trong vòng 1 ngày
-
Độ khó 4/5 3-5 ngày Mức phù hợp với người mới 55/100
Maintainer thường phản hồi trong vòng 1 ngày
-
Độ khó 5/5 Hơn một tuần Mức phù hợp với người mới 15/100
Maintainer thường phản hồi trong vòng 1 ngày
-
Độ khó 4/5 3-5 ngày Mức phù hợp với người mới 35/100
Maintainer thường phản hồi trong vòng 1 ngày
Tất cả issue của apache/hugegraph
Issue tương tự
-
ScyllaDB Manual: 3 broken linksĐang mởlink-check link-check:manual
Độ khó 2/5 1-3 giờ Mức phù hợp với người mới 85/100
-
Độ khó 1/5 Dưới một giờ Mức phù hợp với người mới 91/100
open-telemetry/opentelemetry-java#8870 ·
Maintainer thường phản hồi trong vòng 1 ngày
-
P2 testing
Độ khó 1/5 Dưới một giờ Mức phù hợp với người mới 90/100
Maintainer thường phản hồi trong vòng 1 ngày
-
enhancement javascript
Độ khó 2/5 1-3 giờ Mức phù hợp với người mới 78/100
Maintainer thường phản hồi trong vòng 1 ngày
-
area/core kind/bug status/triage team/core-shared
Độ khó 2/5 1-3 giờ Mức phù hợp với người mới 82/100
Maintainer thường phản hồi trong vòng 1 ngày