[Bug] Docker entrypoint auth bootstrap is unsafe for mounted and upgraded configs
Maintainers usually reply within 1 day
Nobody has claimed this yet.
Assessment
- Difficulty
- 5/5
- Estimated time
- Over a week
- Newbie friendliness
- 45/100
Research direction
Start with docker-entrypoint.sh and bin/enable-auth.sh to trace the current authentication bootstrap and property rewriting paths. Then inspect the proposed config CLI scope, the entrypoint test suite, and docker-build-ci.yml path filters. Done means mounted and upgraded configurations are handled consistently, secrets are not exposed as process arguments, and the listed shell tests cover the entrypoint contract.
Written by the indexing model from the issue text.
Description
Problem
The Docker entrypoint bootstraps authentication with grep/sed against
conf/rest-server.properties. That works for the shipped defaults it was
written for, but not for mounted configs, upgraded volumes, or any value whose
encoding differs between shell and HugeConfig.
Concrete cases, most of them raised during review of #3119:
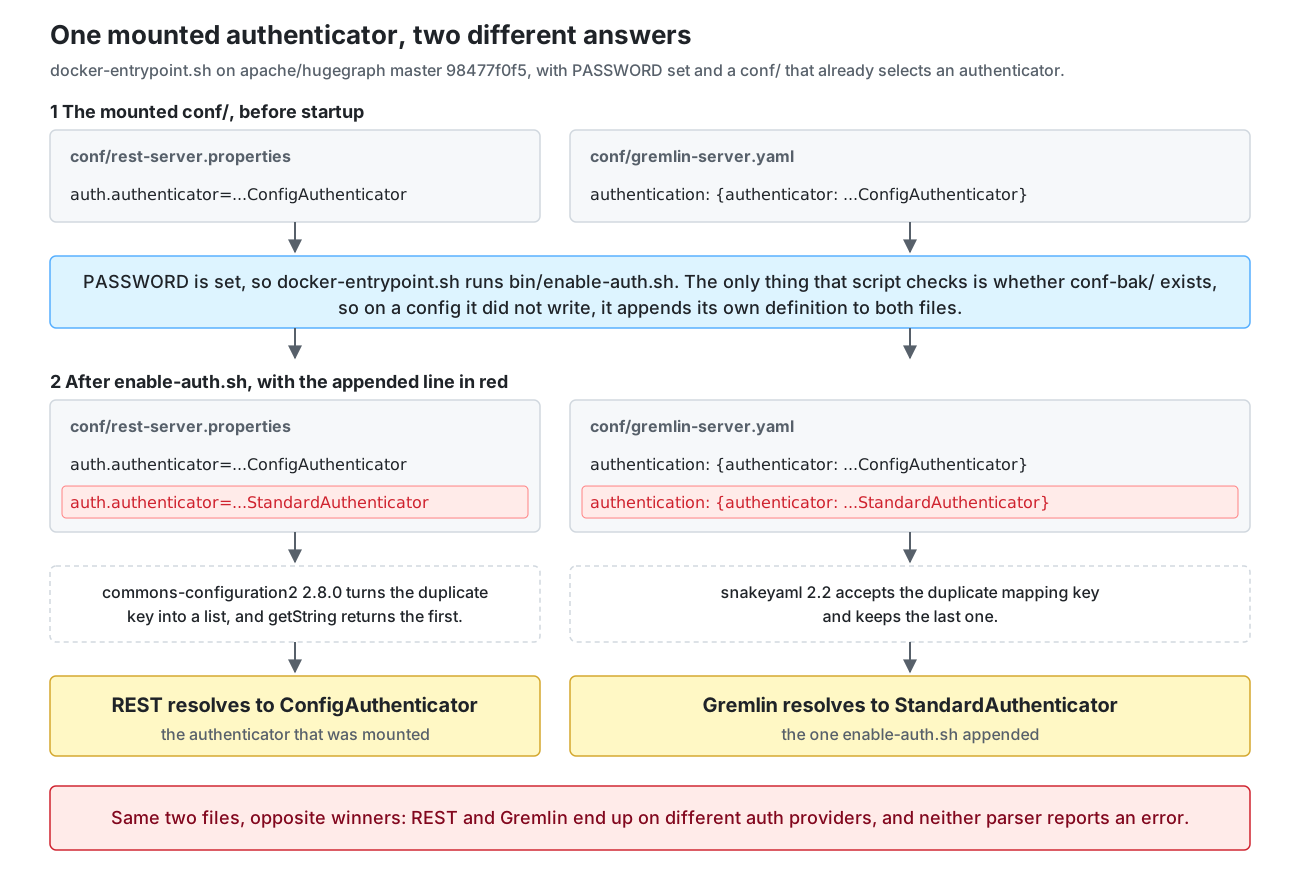
- Gremlin and REST can end up on different auth providers. The check is a
presence-onlygrepforauth.authenticator, so a config that already has
the REST property but not the Gremlin side is treated as fully configured. - A pre-existing authenticated volume can fail its first startup after
upgrade. A legacy volume can carrydocker/init_completewhile the
bootstrap state the entrypoint now expects is absent. PASSWORDis observable. It is currently handed to Java as a command-line
argument, which puts it inpsoutput for every process in the container.sedrewriting does not implement the Java properties grammar. Escaped
keys,:and whitespace separators, continuations, and duplicate logical
definitions are all read differently byHugeConfigthan by the entrypoint.
Concretely,set_propdetects onlykey=, so a mounted config using:
gets a second logical definition appended andHugeConfigthen rejects the
file as a list. This affectsbackendandpd.peersas well as
init_store.enabled, so the fix should cover all of them together.PASSWORDsilently does nothing when init-store is skipped.init-store
reads it from stdin, and the disabled path returns before that, so the admin
is created on the PD startup path fromauth.admin_pa— public defaultpa.
#3119 documents this and warns at runtime; it does not fix it.
The first case, as it stands on master 98477f0f5: the entrypoint no longer
greps for auth.authenticator itself, it calls bin/enable-auth.sh whenever
PASSWORD is set, and that script gates only on whether conf-bak/ exists.
On a config it did not write, it appends a second definition to both files,
and the two parsers disagree about which one wins.
Proposal
Move property reading and writing off grep/sed and onto the same
Commons Configuration path HugeConfig uses, so both sides agree on encoding,
and let the entrypoint delegate auth classification to it.
Rough shape:
- a small
ConfigToolCLI for typed get/set against a properties file,
preserving comments, file mode, and inode for mounted configs; - entrypoint uses it instead of
grep/sed, and stops passing secrets as
process arguments; - auth bootstrap becomes explicit about mounted, upgraded, and custom
authenticator cases rather than inferring from one key's presence; - a shell test suite covering the entrypoint contract, wired into
docker-build-ci.yml.
Scope
In scope: docker-entrypoint.sh, the new config CLI and its wrapper, the
entrypoint test suite, and the workflow path filters that run it.
Out of scope: the init_store.enabled option and its gate (#3118 / #3119),
Helm chart structure, and GraphManager behavior.
Context
This work originally shared a branch with #3119. That made a ~2,900-line diff
covering two unrelated ideas, so it was split out to keep each reviewable on
its own. #3119 now carries only the option, the gate, the env mapping, and the
init-flag guard.
Visual summary
- Dominant language
- Java
- Stars
- 3.2k
- Forks
- 637
- Avg merge
- 3d 18h
- Merged PRs (30d)
- 23
Getting set up
First steps
- Read the whole issue, then the project's contributing guide.
- Comment on the issue to say you are picking it up — it saves two people doing the same work.
- Fork the repository and make your change on a branch.
- Open a pull request that references the issue number.
More from apache/hugegraph
-
Difficulty 2/5 1-3 hours Newbie friendliness 70/100
apache/hugegraph#3231 · 1 comment ·
Maintainers usually reply within 1 day
-
bug
Difficulty 2/5 1-3 hours Newbie friendliness 64/100
apache/hugegraph#3142 · 7 comments ·
Maintainers usually reply within 1 day
-
Difficulty 4/5 3-5 days Newbie friendliness 35/100
Maintainers usually reply within 1 day
-
Difficulty 5/5 Over a week Newbie friendliness 30/100
apache/hugegraph#3238 · 2 comments ·
Maintainers usually reply within 1 day
-
feature
Difficulty 3/5 1-2 days Newbie friendliness 65/100
apache/hugegraph#3236 · 3 comments ·
Maintainers usually reply within 1 day
All issues in apache/hugegraph
Similar issues
-
bug
Difficulty 2/5 1-3 hours Newbie friendliness 84/100
Maintainers usually reply within 1 day
-
bug
Difficulty 2/5 1-3 hours Newbie friendliness 82/100
Maintainers usually reply within 1 day
-
ci-failure-cause test-failure
Difficulty 2/5 1-3 hours Newbie friendliness 72/100
Maintainers usually reply within 1 day
-
enhancement
Difficulty 2/5 1-3 hours Newbie friendliness 65/100
nextcloud/notes-android#3367 ·
Maintainers usually reply within 1 day
-
:wave: team-triage a:chore in:isolated-projects in:kotlin-dsl
Difficulty 2/5 1-3 hours Newbie friendliness 78/100
Maintainers usually reply within 1 day