Include nonce attribute for Content Security Policy
Nobody has claimed this yet.
Assessment
- Difficulty
- 3/5
- Estimated time
- 1-2 days
- Newbie friendliness
- 45/100
- Issue type
- Feature
- Clarity
- Mostly clear
- Activity status
- Stale
- Tech stack
- javascript
Research direction
Review the linked enhance-starter-project issue and the CSP error shown here to understand when a nonce is available and which form elements need it. Locate the form-element rendering code and its existing tests, then verify that nonce-bearing output includes the nonce attribute without changing output when no nonce is available.
Written by the indexing model from the issue text.
Description
See https://github.com/enhance-dev/enhance-starter-project/issues/12
When a nonce is available, form-elements should include that nonce as an attribute to prevent errors like in this screenshot:
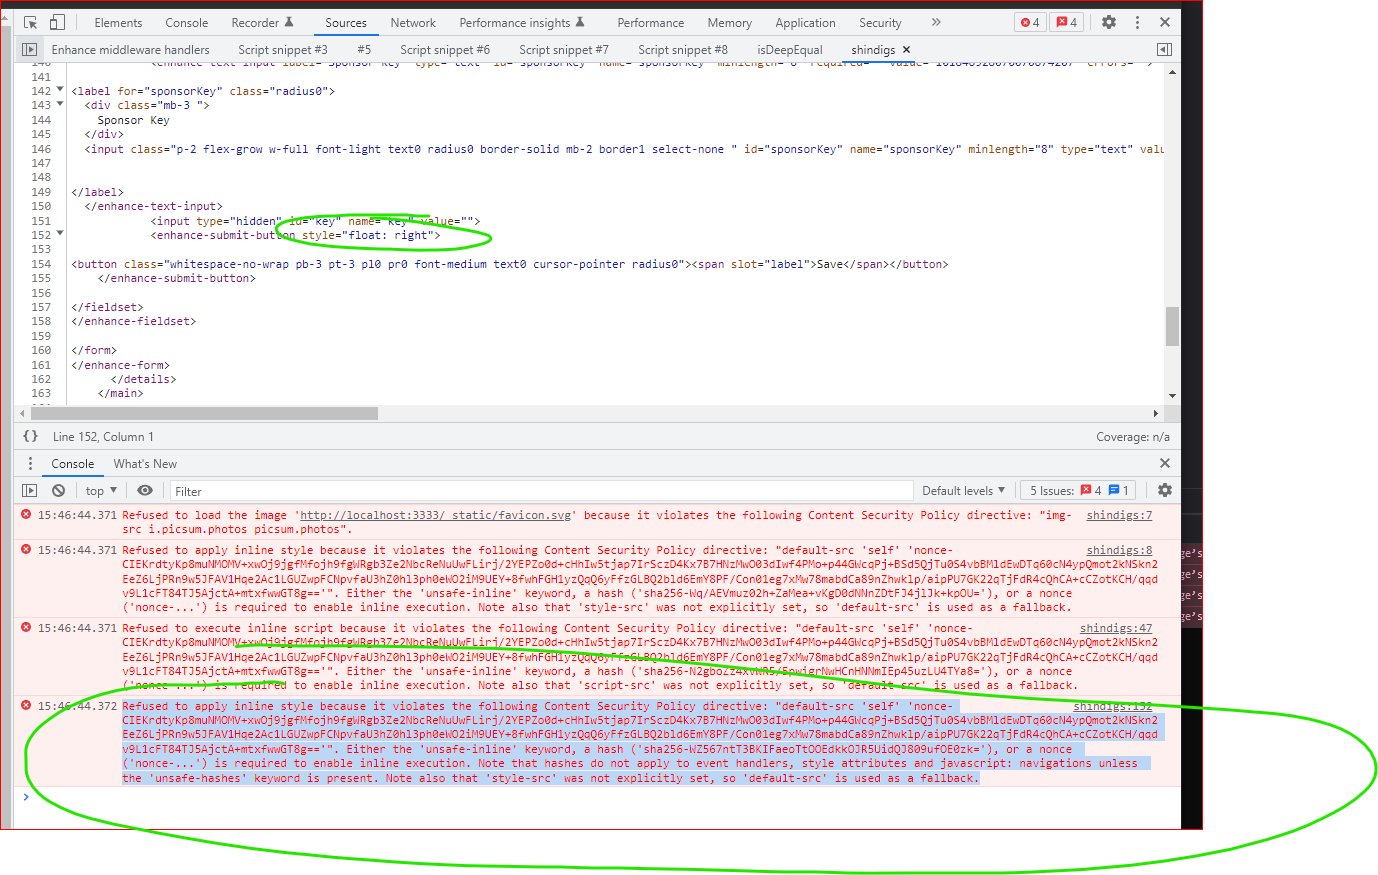
Refused to apply inline style because it violates the following Content Security Policy directive: "[omitted for brevity]". Either the 'unsafe-inline' keyword, a hash ('sha256-WZ567ntT3BKIFaeoTtOOEdkkOJR5UidQJ809ufOE0zk='), or a nonce ('nonce-...') is required to enable inline execution.
- Dominant language
- JavaScript
- Stars
- 4
- Forks
- 1
- PR merge metrics
- No merged PRs in 30d
Contributor guide
First steps
- Read the whole issue, then the project's contributing guide.
- Comment on the issue to say you are picking it up — it saves two people doing the same work.
- Fork the repository and make your change on a branch.
- Open a pull request that references the issue number.
Similar issues
-
bot:ai-assisted component:compact-js status:untriaged
Difficulty 2/5 1-3 hours Newbie friendliness 84/100
midnightntwrk/midnight-sdk#403 ·
-
Difficulty 1/5 Under an hour Newbie friendliness 92/100
-
Difficulty 1/5 1-3 hours Newbie friendliness 86/100
DavidAnson/markdownlint-cli2#940 ·
-
documentation
Difficulty 2/5 1-3 hours Newbie friendliness 88/100
githubnext/gh-aw-workshop#3692 ·
-
agent/guide documentation hive/hosted-available-lke648397-260827-5n31
Difficulty 2/5 1-3 hours Newbie friendliness 90/100